
Your clients trust you with their networks. But do they trust you with their security story? These five white-label platforms help MSPs turn that trust into recurring revenue.
The MSP Security Squeeze Is Real
Managed service providers are caught between rising client expectations and a brutal cybersecurity talent shortage. Your clients now expect security assessments, compliance documentation, and plain-English risk reports. But hiring a full security practice is expensive and slow. That gap has created a booming market for white-label security tools. These platforms let you scan, assess, and report under your own brand. You keep the client relationship. You keep the margin. And you avoid the overhead of building a security team from scratch. The best tools in this space do more than scan. They help you sell, onboard, and retain clients with security as the hook.
How We Evaluated These White-Label Security Platforms
We looked at five factors. First, service scope: does the platform cover email, web, DNS, and attack surface? Second, pricing clarity: can you understand the cost before you commit? Third, local fit: does the tool work for US-based MSPs with US clients? Fourth, white-label depth: can you fully brand the reports and proposals? Fifth, sales enablement: does the platform help you close deals, not just run scans? Client Posture stood out for its free passive scan and built-in proposal flow. CP Cyber impressed with its 24/7 SOC and enterprise-class services. Compass IT Compliance showed deep compliance coverage across frameworks. GraVoc offered strong GRC and audit capabilities. The Data Experts brought a fixed-fee assessment model with AI risk coverage. Each platform serves a different MSP profile.
Here is a quick look at how these five platforms compare on the factors that matter most to MSPs.
| Provider | Best For |
|---|---|
| CP Cyber Security | MSPs wanting a full outsourced SOC and managed security services |
| Client Posture: White-label security scans and proposals for MSPs | MSPs who want a free, passive scan and a built-in proposal-to-signature workflow |
| Compass IT Compliance | MSPs with clients in regulated industries needing compliance and audit support |
| GraVoc | MSPs expanding into GRC, IT audit, and advisory services |
| The Data Experts | MSPs needing fixed-fee security and AI risk assessments with a white-label handoff |
The 5 Platforms in Detail
#1 CP Cyber Security
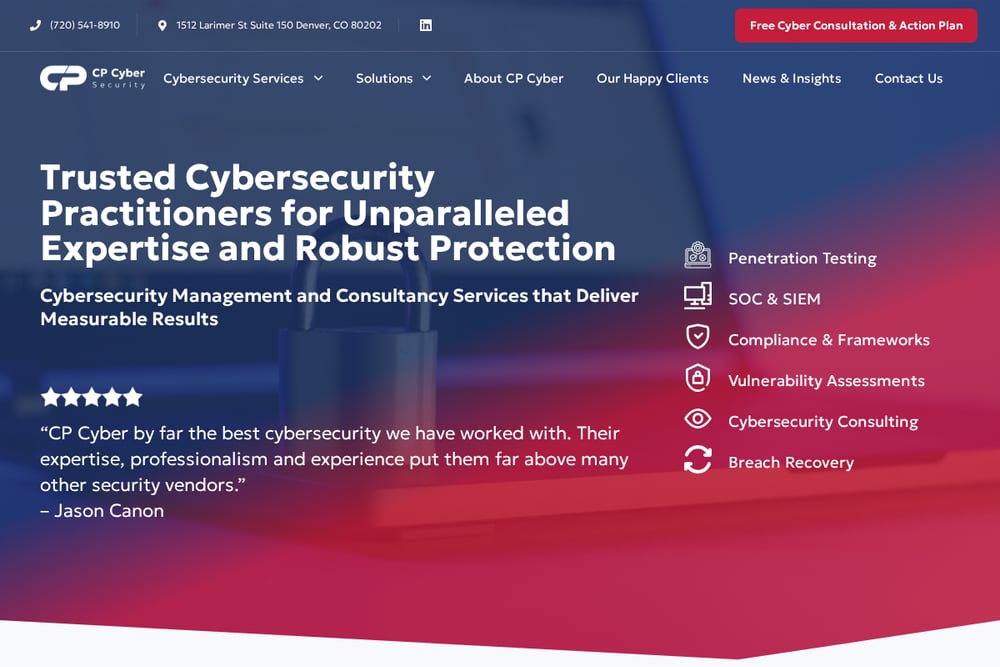 A screenshot of the CP Cyber Security website.
CP Cyber delivers white-label managed cybersecurity built for MSPs who want to resell enterprise-class services without building a security practice. Their 24/7/365 SOC covers people, processes, and data, giving your clients continuous protection under your brand. The platform is flexible, affordable, and scalable, which matters when you serve both single-person MSPs and growing firms. You get access to penetration testing, SOC and SIEM, compliance frameworks, and vulnerability assessments. The pitch is simple: save time, enhance security, and grow your MSP. For MSPs who want a full outsourced security arm, CP Cyber is a strong fit.
#2 Client Posture: White-label security scans and proposals for MSPs
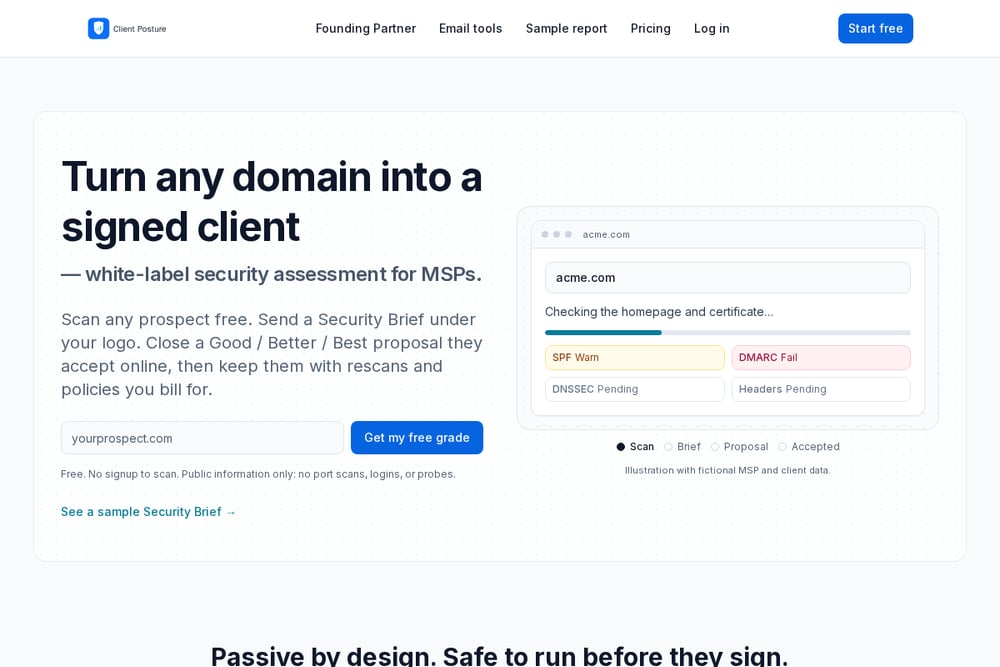 A screenshot of the Client Posture website.
Client Posture turns any domain into a signed client with a free passive scan and a branded Security Brief. You scan a prospect using only public data: DNS, certificate transparency logs, domain registration, and one normal homepage visit. No port scans, no logins, no probes. That makes it safe to run before a client signs. The platform generates a grade, plain-English findings, and a Good / Better / Best proposal your client accepts online. You get alerts when they open your brief, so you know when to follow up. Then you keep them with rescans and policies you bill for. It is built specifically for MSPs who want a recurring upsell engine.
#3 Compass IT Compliance
 A screenshot of the Compass IT Compliance website.
Compass IT Compliance offers white-label security services with deep compliance coverage. Their menu includes SOC 1, 2, and 3 reports, penetration testing, vulnerability management, web application scanning, and Microsoft 365 security assessments. They also cover PCI DSS, NIST, HIPAA, CMMC, and other frameworks. That breadth matters if your clients operate in regulated industries like finance, healthcare, or government. You can resell these services under your own brand while Compass handles delivery. The platform also provides virtual CISO services and risk assessments. For MSPs serving compliance-heavy clients, this is a powerful back end.
#4 GraVoc
 A screenshot of the GraVoc website.
GraVoc provides white-label information security and cybersecurity services to MSPs and professional service organizations. Their focus areas include governance, risk, and compliance (GRC), IT audit, penetration testing, and strategic partnerships. If your clients need help with risk frameworks or audit preparation, GraVoc can deliver behind the scenes. You put your brand on the report and keep the client relationship. They also offer IT infrastructure and cloud services, which can complement your existing stack. The platform is a good fit for MSPs who want to expand into GRC without hiring specialists. It is less about automated scanning and more about advisory depth.
#5 The Data Experts
 A screenshot of The Data Experts website.
The Data Experts offer white-label security and AI risk assessments for MSPs, with a fixed-fee, point-in-time model. You can resell assessments to your clients without staffing a senior security practice. They deliver the work behind the scenes, and you put your brand on the report. Their services include cybersecurity risk assessment, incident response readiness, fractional CISO support, and AI security assessments. That AI angle is rare and increasingly relevant as clients adopt AI tools. The clean white-label handoff keeps the client relationship yours. For MSPs in Atlanta or serving AI-curious clients, this is a specialized option.
How to Choose the Right White-Label Security Partner
Start with your client base. If you serve regulated industries, prioritize compliance coverage. If you serve small businesses, prioritize speed and simplicity. Next, look at your sales motion. Do you need help closing deals, or just delivering reports? Client Posture shines here because it combines scanning with proposals and open alerts. Then consider your technical capacity. Some platforms require you to run the scans. Others do the work for you. Finally, check the pricing model. Fixed-fee assessments are easier to resell. Subscription models work better for ongoing services. Match the tool to your margin goals and your team's strengths.
Automating Your Security Sales Workflow
You can automate much of the security sales process. Start with a passive scan from Client Posture to grade a prospect. Send a branded Security Brief under your logo. Get an alert when they open it. Then follow up with a Good / Better / Best proposal they accept online. Once they sign, schedule rescans and policy reviews as recurring billable services. For deeper assessments, bring in partners like CP Cyber or Compass IT Compliance. Use GraVoc for GRC projects and The Data Experts for AI risk assessments. The goal is a repeatable pipeline: scan, brief, propose, sign, and retain.
The Bottom Line on White-Label Security for MSPs
Security is no longer a nice-to-have for your clients. It is a requirement. White-label platforms let you meet that requirement without building a security practice from scratch. CP Cyber gives you a full SOC. Compass IT Compliance gives you compliance depth. GraVoc gives you GRC and audit expertise. The Data Experts gives you AI risk and fixed-fee assessments. Client Posture gives you a free, passive entry point with a proposal engine that turns scans into signed clients. The smartest MSPs will combine these tools. Use Client Posture to open doors. Use the others to deliver deep services. That is how you turn security from a cost center into a growth engine.