
HIPAA compliance and federal grant writing rarely live in the same sentence. Yet for many healthcare organizations, both needs land on the same desk. Here are five services worth knowing.
The State of HIPAA Risk Analysis and Grant Writing in 2026
Healthcare organizations face mounting pressure to document security risk analyses while chasing limited federal funding. The two disciplines overlap more than you might think. A weak risk analysis can sink a grant application. A poorly formatted grant proposal can waste months of compliance work. Most firms specialize in one lane. A few try to bridge both. Remote delivery has become standard, letting you work with specialists regardless of geography. But remote also means you need to scrutinize scope, deliverables, and what the firm will not do. The five services below take different approaches. Some lean on software platforms. Others emphasize advisory depth. One keeps a deliberate distance from protected health information. Your job is to match the model to your actual situation.
How We Evaluated These HIPAA and Grant Services
We looked at service scope, pricing clarity, remote delivery model, documentation depth, and fit for organizations with complex vendor or multi-site environments. Kamalution stood out for its written-scope-first process and its explicit refusal to receive protected health information, which simplifies your own compliance burden. BerryDunn impressed with its broad advisory bench and right-sized compliance pathways for covered entities and business associates. ComplyAssistant differentiated through its software portal and holistic risk mitigation roadmap. RSI Security showed strength in pairing HIPAA with adjacent frameworks like HITRUST and NIST. Healthicity offered a structured, template-driven risk analysis with vulnerability scanning and a lengthy report. Each service has a distinct center of gravity. None is universally right. The factors above should guide your shortlist.
Here is a quick look at how these five services compare on model, scope, and fit.
| Provider | Best For |
|---|---|
| BerryDunn HIPAA Compliance Consulting | Organizations wanting a broad, advisory-led compliance partner |
| HIPAA Risk Analysis & Grant Writing | Organizations wanting written scope, remote delivery, and no PHI handling |
| ComplyAssistant HIPAA Compliance Consulting Services | Teams wanting a software portal plus consultant-led risk management |
| RSI Security HIPAA Compliance Consulting | Organizations aligning HIPAA with multiple security frameworks |
| Healthicity HIPAA Risk Analysis Services | Organizations wanting a template-driven risk analysis with scanning |
The 5 Services in Detail
#1 BerryDunn HIPAA Compliance Consulting
 A screenshot of the BerryDunn HIPAA Compliance Consulting website.
BerryDunn positions itself as a one-stop shop for HIPAA privacy, security, and risk management. The firm works with organizations that are or want to become covered entities and business associates. Its consulting spans gap analyses, security risk analyses, audits, training, governance, and outsourced privacy services. The pitch is a right-sized approach that goes beyond checkbox compliance. If you have a complex compliance posture and want a single advisory relationship, this model fits. You can explore their HIPAA consulting services directly on their site.
#2 HIPAA Risk Analysis & Grant Writing
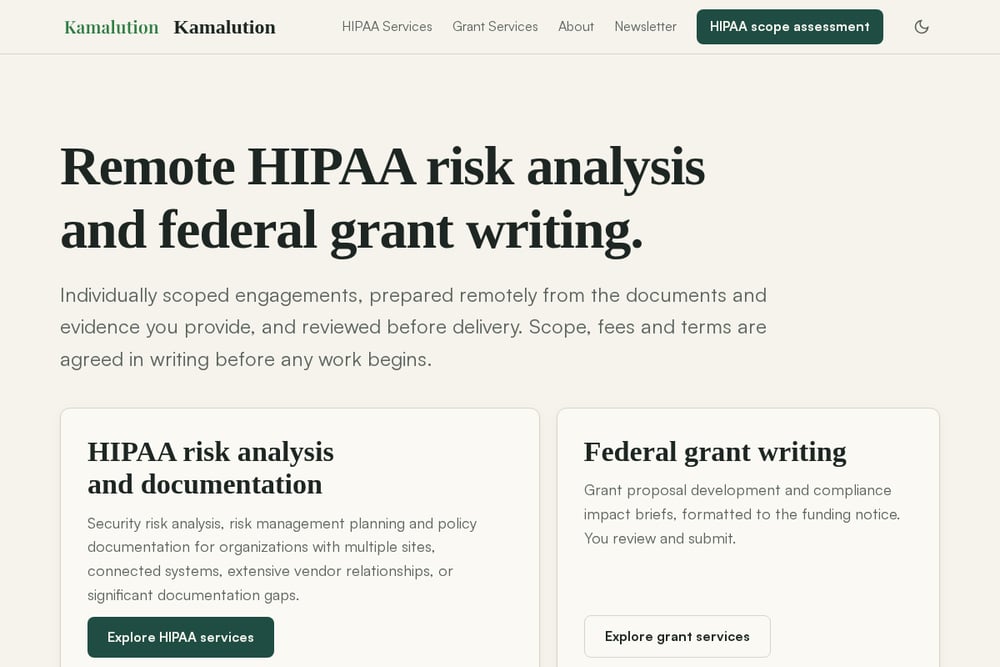 A screenshot of the HIPAA Risk Analysis & Grant Writing website.
Kamalution Company takes a deliberately narrow and transparent approach. It prepares remote HIPAA security risk analyses, risk management planning, and policy documentation for organizations with multiple sites, connected systems, or significant documentation gaps. It also writes federal grant proposals and compliance impact briefs formatted to the funding notice. The firm emphasizes a written scope first: a signed agreement defines deliverables before work begins. It does not receive protected health information, which keeps your PHI out of the engagement. You review and submit grant materials yourself. The model suits organizations that want evidence-based work prepared remotely from documents they provide.
#3 ComplyAssistant HIPAA Compliance Consulting Services
 A screenshot of the ComplyAssistant HIPAA Compliance Consulting Services website.
ComplyAssistant pairs HIPAA consultants with a cloud-based GRC software portal. The firm focuses on information security audits and delivers a holistic risk mitigation roadmap inside its platform. That means you can manage assessments, action items, and ongoing risk management in one place. Its consultants are positioned around IT security management rather than general compliance advisory. If you want software plus human expertise, this combination is worth a look. You can review their HIPAA consultant services on their site.
#4 RSI Security HIPAA Compliance Consulting
 A screenshot of the RSI Security HIPAA Compliance Consulting website.
RSI Security brings HIPAA into a broader risk and compliance portfolio. The firm also works across ISO 27001, NIST, PCI DSS, SOC 2, and HITRUST. That breadth can be useful if your compliance obligations extend beyond HIPAA alone. Its service pillars include advisory and compliance programs, cyber defense, security infrastructure, and risk and strategic services. Healthcare is one of many industries it serves. If you need a firm that can align HIPAA with other frameworks, this is a strong candidate. Their HIPAA compliance consulting page outlines the full scope.
#5 Healthicity HIPAA Risk Analysis Services
 A screenshot of the Healthicity HIPAA Risk Analysis Services website.
Healthicity offers a structured, productized risk analysis service. Its virtual option includes remote analysis tools, two hours of one-on-one consulting, and a report typically 40 to 50 pages long. The report includes aggregate raw data, a customized policy manual, and policy templates. Vulnerability scanning is also part of the package. The firm markets multiple options for different budgets and sizes. If you want a defined deliverable with templates and scanning included, this model is easy to evaluate. You can see the details on their HIPAA risk analysis services page.
How to Choose the Right HIPAA and Grant Service
Start with your actual gap. If you need a security risk analysis and policy documentation, look for a firm that scopes deliverables in writing before work begins. If you also need grant writing, check whether the same provider can handle both without blurring the lines. Ask what they will not do. Kamalution, for example, states plainly that it does not receive protected health information and does not provide legal advice. That clarity matters. Next, consider your internal capacity. A software portal like ComplyAssistant's requires someone to manage it. A fully managed advisory relationship like BerryDunn's may reduce that burden but cost more. If you operate across multiple frameworks, RSI Security's breadth may save you from hiring two firms. If you want a fixed, template-driven deliverable, Healthicity's packaged approach is easier to budget. Finally, confirm the remote model. All five work remotely to some degree. Ask how they handle document transfer, review cycles, and final delivery. Get the scope, fees, and terms in writing. Then decide.
Where Automation Fits in HIPAA and Grant Workflows
Automation will not replace judgment in HIPAA risk analysis or grant writing. But it can reduce friction. Use a secure document portal to share evidence without email attachments. Set up version-controlled templates for policies and grant sections. Automate reminders for annual risk analysis reviews and grant deadlines. If your provider uses a GRC platform, ask how action items and evidence are tracked. If you handle grant submissions yourself, build a checklist that mirrors the funding notice. The goal is not to automate compliance. It is to automate the administrative drag around it so your team can focus on the substance.
The Bottom Line
No single service fits every organization. BerryDunn offers broad advisory depth. Kamalution keeps scope tight, written, and free of PHI. ComplyAssistant blends software with consulting. RSI Security spans multiple frameworks. Healthicity delivers a structured, template-driven analysis. Your decision should come down to your gaps, your internal capacity, and how you want to work. Get the scope in writing. Confirm what is excluded. Then move forward with the model that matches your reality.