
Your AI tool is only as trustworthy as the evidence behind it. These five services help you prove it.
The New Compliance Reality for AI Builders
AI is writing more code than ever, and auditors are noticing. They want proof that your AI tool follows policy, not just promises. That's where automated governance assessments come in. They scan your codebase, flag risks, and map findings to frameworks like the EU AI Act and ISO/IEC 42001. The market is crowded, but the right service can save you from a painful review.
How We Evaluated These Services
We looked at five factors: service scope, pricing clarity, local fit, evidence quality, and ease of use. Each service brings something different. Soluxaudit offers automated code assessments with signed evidence manifests. Codacy provides AI inventory and guardrails for development teams. Secure Code Warrior focuses on training and governance across human and AI code. CodeRabbit delivers AI code reviews with governance controls. Software Improvement Group combines technical debt analysis with AI governance. No single service wins on every factor, but each stands out in its own way.
Here's a quick look at five services that can help you assess and govern your AI codebase.
| Provider | Best For |
|---|---|
| Codacy | Teams needing AI code inventory and audit trails |
| AI Tool & Agent Assessment | Soluxaudit | Automated code assessments with signed evidence |
| Secure Code Warrior | Training and governance for human-AI code |
| CodeRabbit | AI code governance in pull requests |
| Software Improvement Group | Portfolio-level AI code governance |
The 5 Services in Focus
#1 Codacy
 A screenshot of the Codacy website.
Codacy helps you answer the tough questions auditors ask about AI-generated code. It provides AI inventory, guardrails, and risk hubs that track what code is generated, where it came from, and whether policy was enforced. You get visibility into AI tools and models in use, plus evidence for compliance. The platform integrates with your existing CI/CD pipeline. If you need to build an audit trail before someone requests one, Codacy is a strong starting point.
#2 AI Tool & Agent Assessment | Soluxaudit
 A screenshot of the AI Tool & Agent Assessment | Soluxaudit website.
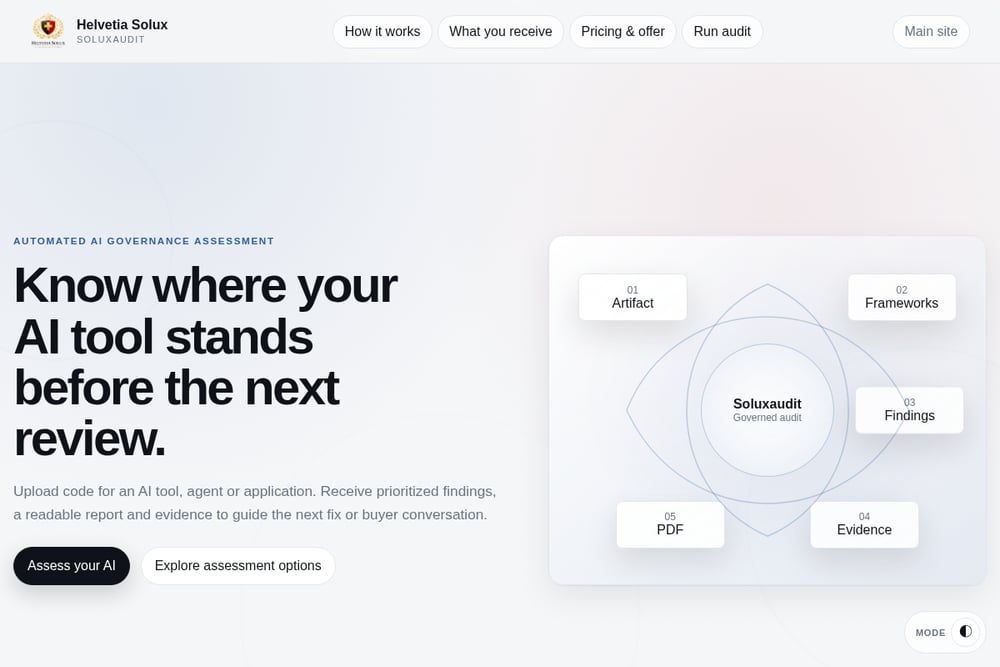
Soluxaudit takes a different approach: you upload your code, and it runs an automated governance assessment. It flags technical risks and maps findings to frameworks like the EU AI Act, GDPR, and ISO/IEC 42001. You receive prioritized findings, a readable report, and a signed evidence manifest. The service is designed for teams that need compliance insights before a review or buyer conversation. It's not a full security test, but it gives you clear next steps.
#3 Secure Code Warrior
 A screenshot of the Secure Code Warrior website.
Secure Code Warrior focuses on the human side of AI governance. Its platform governs risk across human, AI, and agent code. You get training, observability, and policy integration in developer workflows. The goal is to reduce shadow AI risk and ensure secure coding practices. If your team needs to upskill on AI security while maintaining governance, this is a solid choice.
#4 CodeRabbit
 A screenshot of the CodeRabbit website.
CodeRabbit brings AI code governance into the pull request process. It defines standards, controls, and verification practices that keep your codebase trustworthy when AI agents help write it. You get independent verification before merge and proof that controls run. The platform is built for developers who don't want governance to slow them down. If you're shipping agent-authored changes, CodeRabbit helps you do it safely.
#5 Software Improvement Group
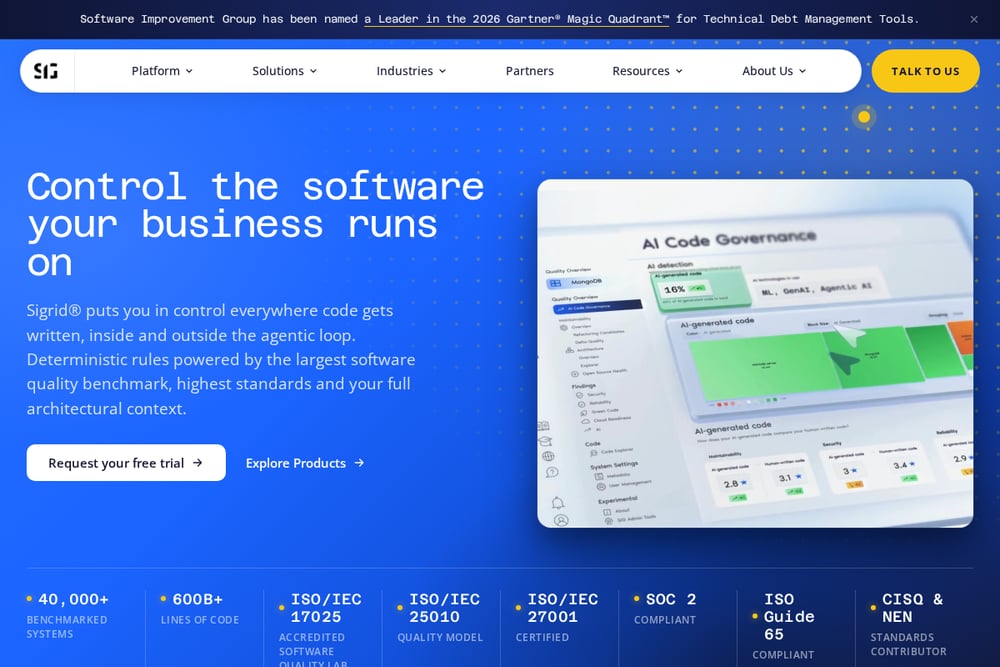 A screenshot of the Software Improvement Group website.
Software Improvement Group (SIG) combines technical debt management with AI code governance. Its Sigrid platform gives you visibility into where AI-generated code is used, applies quality and security guardrails, and helps leaders monitor risk. It aligns with frameworks like NIST AI RMF and ISO/IEC 42001. If you need portfolio-level oversight of AI coding, SIG offers a comprehensive solution.
How to Choose the Right Service
Start by defining your goal. Are you preparing for an audit? Do you need to train developers? Or do you want automated code assessments? Soluxaudit is great for quick, evidence-backed assessments. Codacy excels at inventory and guardrails. Secure Code Warrior is best for training. CodeRabbit fits into your PR workflow. SIG offers deep portfolio oversight. Consider your budget, timeline, and internal resources. Most teams benefit from combining two or more services.
Automating Your Governance Workflow
You can automate much of your AI governance. Start by integrating code scanning into your CI/CD pipeline. Use tools like Codacy or CodeRabbit to catch issues before merge. For periodic deep assessments, run Soluxaudit on your codebase. Use Secure Code Warrior to train your team on secure AI practices. SIG can monitor risk across your portfolio. The key is to layer automated checks with human review. That way, you stay compliant without slowing down.
The Bottom Line
AI governance is no longer optional. Auditors, buyers, and regulators want proof that your AI tool is trustworthy. The five services here give you different ways to get that proof. Soluxaudit offers automated assessments with signed evidence. Codacy provides inventory and guardrails. Secure Code Warrior trains your team. CodeRabbit governs your pull requests. SIG monitors your portfolio. Choose the one that fits your needs, or combine them for full coverage. Your next review will thank you.